news
synacktiv.com
On the clock: Escaping VMware Workstation at Pwn2Own Berlin 2025
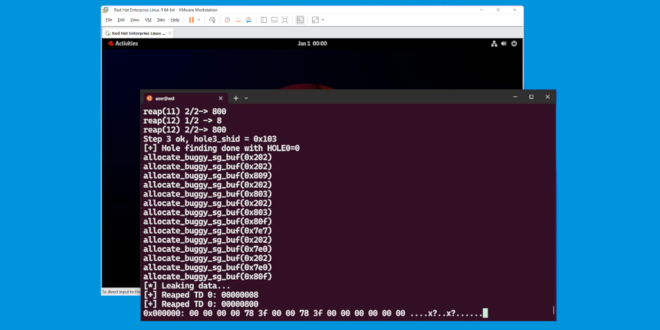
At Pwn2Own Berlin 2025, researchers successfully exploited a Heap-Overflow vulnerability in VMware Workstation's PVSCSI controller implementation, specifically identified as CVE-2025-41238. The exploitation process was complex due to the security mitigations in Windows 11's Low Fragmentation Heap (LFH), which posed significant challenges. The team navigated these obstacles by employing a combination of techniques that included defeating LFH randomization via a timing side-channel, carefully managing an exploitable heap layout, and utilizing the quirks of the vulnerable function to create effective memory manipulation primitives.
The vulnerability allowed for out-of-bounds writes when the guest OS provided more than 512 SCSI command entries, leading to memory corruption. The exploitation involved shaping the heap with two critical objects to control memory behavior effectively. The researchers utilized shaders to spray controlled data, aiding in heap manipulation and ensuring they could execute arbitrary read, write, and code execution.
Despite the initial difficulty, a breakthrough occurred just two days before the event, enabling the exploit to succeed on the first attempt during the live demonstration. The complexity of navigating LFH's strict allocation checks and metadata verification highlighted the intricacies of modern exploitation techniques, showcasing the significant risks associated with peripheral device emulation in virtual environments.
Article timeline
Build this article’s timeline
Extract dated events, key actors, and open questions using the same timeline analysis available in Signal.
Log in to build
Timeline generation is available to signed-in community members.
Primary-source excerpts
Login to contribute excerpts from the source.
Five Ws
🤖 5 AI prefills · all filled
Who
VMware
What
At Pwn2Own Berlin 2025, researchers successfully exploited a Heap-Overflow vulnerability in VMware Workstation's PVSCSI controller implementation, specifically identified as CVE-2025-41238.
When
2025 and 23/01/2026
Where
Berlin and Windows 11
Why
Centers on PVSCSI controller, Heap-Overflow vulnerability, and Windows 11 Low Fragmentation Heap
Login to answer and earn XP for each gap you fill.
VMware Exploit Techniques VMware, PVSCSI, exploit, vulnerability, heap overflow Low Fragmentation Heap Challenges LFH, Windows 11, mitigation, randomization, memory allocation Exploitation Methodology techniques, heap shaping, corruption, timing side-channel, deterministic behavior Pwn2Own Competition Insights Pwn2Own, competition, demonstration, live exploit, security research
Key Phrases:
PVSCSI controller95% Heap-Overflow vulnerability93% Windows 11 Low Fragmentation Heap90% memory manipulation primitives88% timing side-channel85% exploitable heap layout84% S/G segments82% CVE-2025-4123880% deterministic behavior78% shader objects76%
Comments
Login to view and post comments.